The October 2026 Security Crisis: Breaking Down the PHP and Node.js RCE Vulnerabilities & Patch Guide
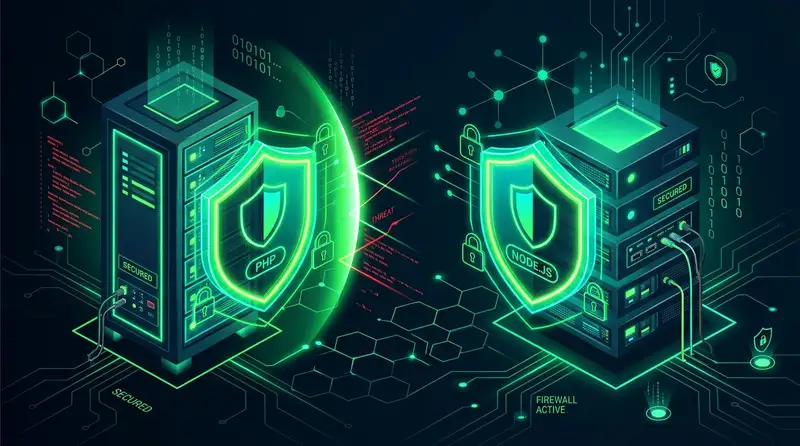
The global web infrastructure landscape faced a historic wave of critical vulnerabilities this week in October 2026. Within days of each other, the core maintainers of both PHP and Node.js issued urgent out-of-cycle security updates addressing remote code execution (RCE) flaws.
For full-stack engineers and DevOps architects managing enterprise platforms—including Magento e-commerce, WordPress networks, Express/Next.js microservices, and API gateways—these vulnerabilities require immediate patching.
Here is a technical architectural breakdown of PHP2Shell and Node2Shell, how they work under the hood, and how to safeguard your production servers today.
Part 1: The PHP "PHP2Shell" Vulnerabilities (CVSS 9.2)
Tracked as CVE-2026-109618 and CVE-2026-109619, these flaws affect the fundamental memory management and process lifecycle of the Zend Engine dating as far back as PHP 5.4.
The Exploit Mechanism:
1. OOM Memory Corruption (CVE-2026-109618):
An attacker transmits a specially constructed multipart POST request containing deeply nested parameters or oversized form boundaries calibrated to trigger PHP's memory_limit. When an Out-of-Memory (OOM) error occurs, PHP executes a longjmp() to unwind execution. However, because request structures were only partially initialized, the engine misinterprets uninitialized memory during cleanup routines.
2. Use-After-Free in Persistent Worker Pools (CVE-2026-109619):
In high-throughput architectures running PHP-FPM, worker processes persist across requests. Internal allocations associated with error tracking and stack backtraces can outlive the terminated request. When the worker receives the subsequent HTTP request, it references dangling pointers before memory pools are reset.
By chaining these two vulnerabilities, unauthenticated remote attackers can hijack worker threads to execute shell commands with the privileges of the web user (www-data or nginx).
PHP Remediation Steps: Upgrade production runtime environments immediately to the patched releases: PHP 8.5 → Update to 8.5.12+* PHP 8.4 → Update to 8.4.27+* PHP 8.3 → Update to 8.3.36+* PHP 8.2 → Update to 8.2.35+*
(Note: Older EOL branches like PHP 7.4 through 8.1 require distribution-level backported patches from repositories like Ondřej Surý or enterprise Linux vendors).
Part 2: The Node.js "Node2Shell" Brotli Flaw (CVE-2026-111497)
The Node.js project published an emergency release resolving 10 vulnerabilities, headlined by CVE-2026-111497 rated as High (CVSS 8.8).
The Exploit Mechanism:
Node.js bundles native Brotli decompression within its node:zlib module. A boundary calculation flaw in the Brotli decoder leads to an out-of-bounds heap write when processing malformed compressed byte sequences.
This vulnerability impacts:
* Web applications decompressing client payloads via middleware (e.g., Express or Fastify parsing Content-Encoding: br).
* Backend microservices utilizing native fetch() or HTTP clients that automatically decompress upstream Brotli payloads.
* Reverse proxy layers and edge lambdas inspecting compressed traffic.
Crafted byte payloads can trigger heap corruption, leading to denial of service (DoS process crashes) or remote arbitrary code execution inside the Node process.
Node.js Remediation Steps: Upgrade to the latest LTS releases: Node.js 24.x (LTS) → Update to v24.22.1+* Node.js 22.x (LTS) → Update to v22.23.4+* Node.js 26.x (Current) → Update to v26.12.1+*
Comparing the October 2026 Vulnerabilities
| Metric | PHP (PHP2Shell) | Node.js (Node2Shell) |
|---|---|---|
| CVE Identifiers | CVE-2026-109618, CVE-2026-109619 | CVE-2026-111497 |
| Severity Score | Critical (CVSS 9.2) | High (CVSS 8.8) |
| Vulnerable Component | Zend Engine OOM & FPM Worker UAF | Bundled Brotli Decoder in node:zlib |
| Attack Vector | Malformed Multipart POST Payloads | Malformed Brotli Compressed Streams |
| Primary Target | PHP-FPM, Apache mod_php, FrankenPHP | Express, Fastify, Next.js API Routes |
Temporary WAF & Gateway Hardening
If your organization cannot deploy container or runtime rebuilds immediately, implement these defensive rules at your Edge / CDN layer (Cloudflare, AWS WAF, or NGINX):
1. Enforce Strict POST Body Limits: Restrict maximum request body size to reduce the likelihood of memory exhaustion attacks:
# In nginx.conf
client_max_body_size 10M;
client_body_buffer_size 128k;
2. Temporary Brotli Inspection / Strip Rule:
If running unpatched Node services behind a reverse proxy, temporarily strip Accept-Encoding: br to force upstream responses and client requests to fallback to standard Gzip until packages are upgraded.
3. Recycle FPM Workers Frequently:
Reduce PHP-FPM pm.max_requests to 500 or 1000 to ensure worker processes are killed and respawned frequently, limiting the attack window for persistent use-after-free states:
; In www.conf (PHP-FPM pool)
pm.max_requests = 500
By applying runtime patches, tightening edge WAF filters, and configuring defensive worker lifecycles, full-stack teams can fully safeguard their infrastructure against these critical automated exploit scans!
Need premium developer consulting?
Let's discuss how we can build API split checkouts, dynamic Next.js interfaces, or speed audits for your business.
Get in TouchRelated Technical Insights
Zero-Downtime E-Commerce Deployments: Blue-Green Deployments, Automated E2E Testing, and Database Migration Safeguards
Tailwind CSS v4.0 Architecture: CSS-First Configuration, Lightning CSS Compilers, and Zero-JS Style Engines